Linux memory-leak tracker that hooks the allocator via LD_PRELOAD, with no shared object ever written to disk.
Tracking down a leak in a long-running Linux process usually means reaching for Valgrind (slow enough to change timing-sensitive behavior) or rebuilding with ASan (needs a recompile and isn't always an option for a binary you don't control the build of). The goal was a zero-recompile, low-overhead way to point at any existing binary and get a leak report on exit.
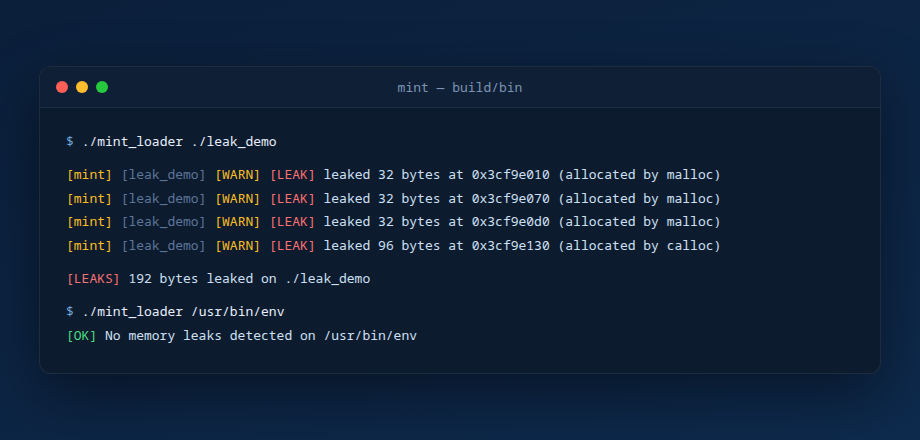
`mint_loader <program> [args...]` runs any binary unmodified and prints a leak summary to stderr on exit — byte count, allocation site, and (optionally) stack trace, with no `.so` left on disk afterward. Nothing to relink, nothing to clean up.
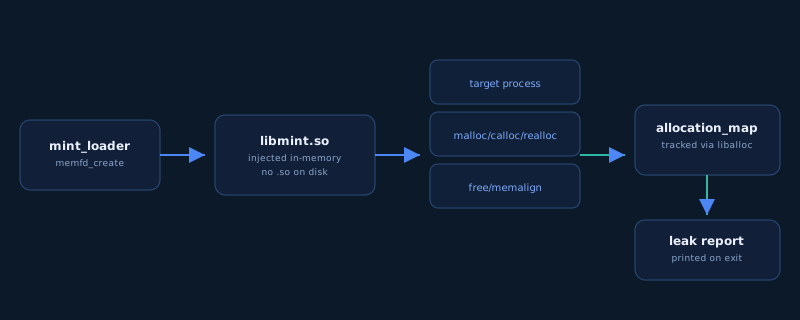
`mint_loader` injects `libmint.so` into the target process's memory via `memfd_create` rather than a path on disk, keeping no artifact behind. The library interposes `malloc`/`calloc`/`realloc`/`free`/`memalign`, tracking live allocations in an internal map built on a vendored allocator (liballoc) so tracking itself doesn't recurse into the hooked functions. On process exit it walks the map and reports anything still outstanding, with optional stack traces via libbacktrace.